CJIS compliance for RMS and CAD software vendors
A records management (RMS) or computer aided dispatch (CAD) vendor holds the most sensitive criminal justice information an agency owns: incident reports, names, warrants and query results. Every county or state buyer asks how you meet the FBI CJIS Security Policy before it signs. Cjis gives your team one workspace to answer: a readiness score by policy area, a register of every person with access, policy templates and a separate report for each agency. Plans are published and start at $49 a month.
What an agency asks an RMS or CAD vendor
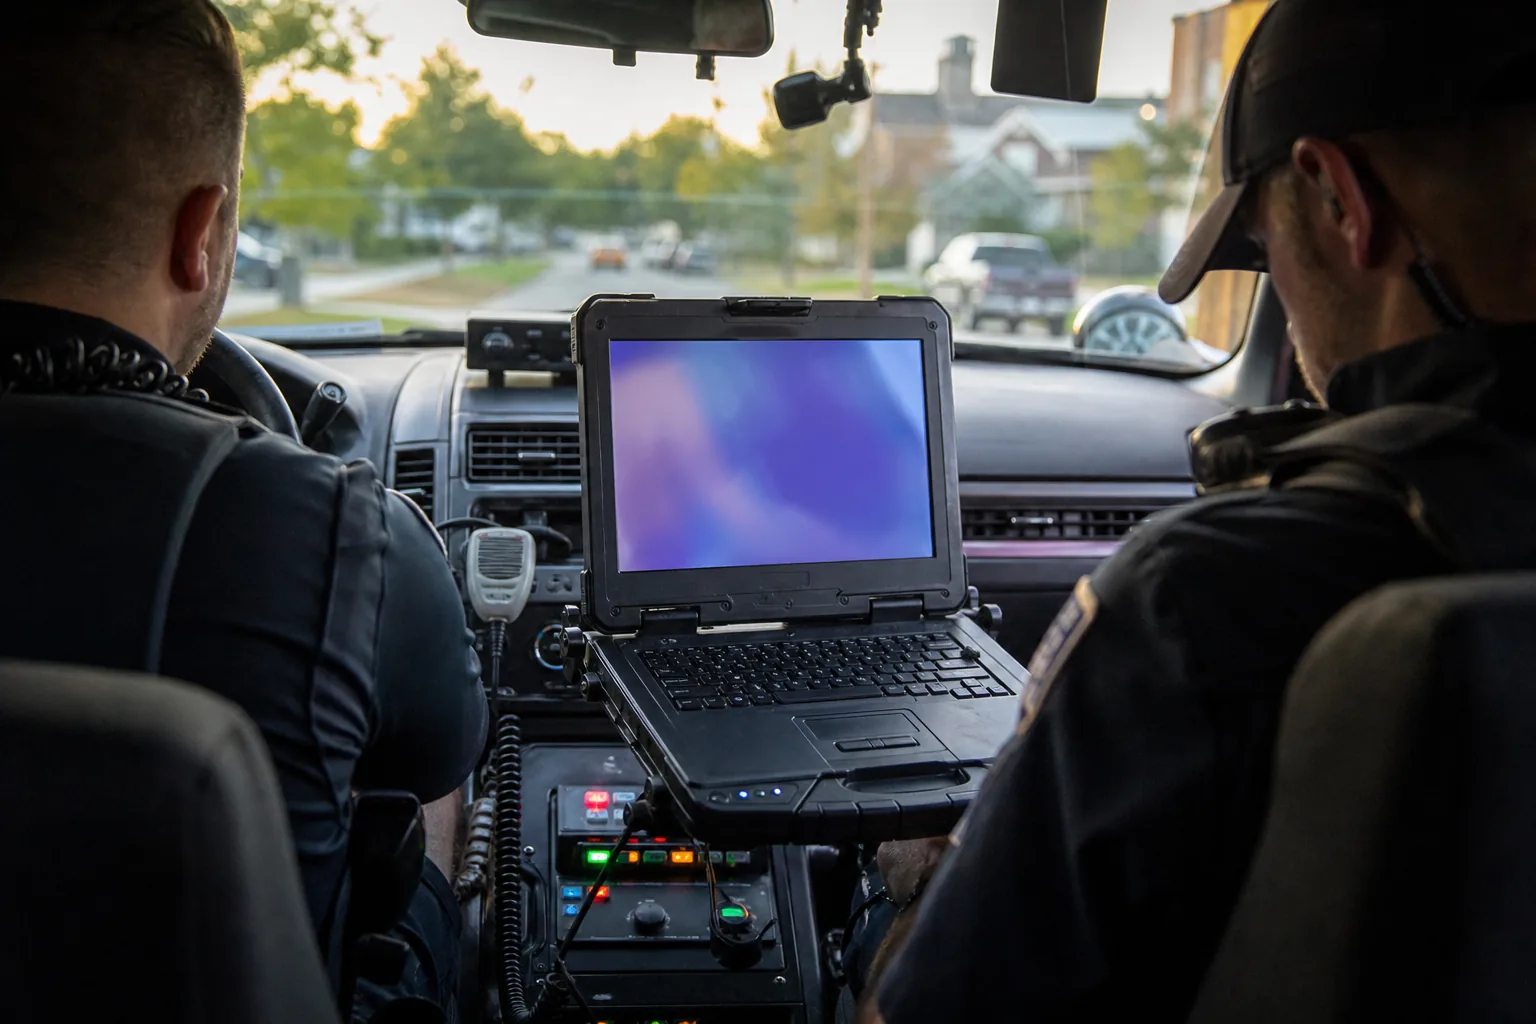
RMS and CAD sit closer to CJI than almost any other public safety product, because they connect to state and NCIC queries through the agency. The agency answers to its state CJIS Systems Agency (CSA), so the RFP pushes the same questions to you: where the system runs, how users authenticate, what you log, who on your staff can see agency data and whether those people passed a fingerprint-based check.
- Hosted or on premises, your install and support staff touch CJI during go live and upgrades
- Each agency signs the CJIS Security Addendum with you, and many states want it for named staff
- The same RFP often asks for a state specific form on top of the policy
Where CJIS touches an RMS or CAD product
For what agencies expect inside the tool itself, see our CJIS compliant software page. Hosting questions are covered in CJIS compliance in AWS, Azure and Microsoft 365.
| Product area | What the policy asks | What you document |
|---|---|---|
| Dispatcher and officer login | Advanced authentication for access to CJI | MFA method, session lock, password rules |
| State and NCIC query interface | Access limited to authorized users, audit trail | Query logging and how long logs are kept |
| Mobile and MDT clients | Encryption in transit, device controls | FIPS validated module, MDM or app controls |
| Hosted database and backups | Encryption at rest, location, provider terms | Region, key custody, backup handling |
| Interfaces with other agencies | Controlled dissemination | Interface list, data flows, agreements |
| Install, upgrade and support | Screened and escorted staff | Fingerprint dates, remote access method |
| Incidents | Notice to the agency and its CSA | Written plan and contact path per agency |
Which of your people count as CJIS personnel
RMS and CAD teams have a long list of people near agency data: implementation engineers who migrate records, trainers who sit at dispatch consoles, tier two support with remote sessions, QA staff with production copies and the field techs who visit a 911 center. Anyone with unescorted logical or physical access to unencrypted CJI needs a fingerprint-based record check and security awareness training, and some states repeat the check for each state. Cjis keeps role, access level, check date by state, training level, expiry and the agencies each person is approved for.
See CJIS background check requirements for what the check involves.
- Import the staff list by CSV and tag who can reach agency data
- Reminders 30 and 7 days before training expires
- Log the day access is removed when someone leaves
One record, a separate report for every county and city
A vendor with fifty agency customers faces a security review at every renewal and every new module. Cjis keeps shared controls and policies once, then a record per agency with its systems, people, agreements and open items. Send a PDF report or a read-only link scoped to one agency, so one sheriff never sees another department's names. Start from the CJIS policy templates for access control, incident response and the system boundary.
- One set of controls mapped to CJIS Security Policy v6.0 and v5.9.5
- Evidence dated and attached to the control it supports
- Open items by agency, so sales sees what blocks a renewal
Ways RMS and CAD vendors keep the CJIS record
Details in the Vanta CJIS alternative comparison and in CJIS compliance consultant vs software.
| Option | Cost | Strength | Weak spot |
|---|---|---|---|
| Spreadsheets and a shared drive | Staff time | Nothing to buy | No reminders, rebuilt for every RFP |
| Cjis | $49 to $999 a month, published | CJIS only, per agency reports, personnel register | No automated cloud tests |
| Multi-framework platform | Quote only | Automated tests across frameworks | CJIS is one framework among many |
| CJIS consultant | Per engagement | State know-how | A snapshot that ages |
Plans that match a public safety sales pipeline
Starter at $49 a month covers one agency report. Team at $199 covers three agency reports and fits a vendor in several active RFPs. Pro at $499 covers 25 agencies, and Enterprise at $999 has no agency limit, which suits an established RMS or CAD vendor with a large customer base. Yearly billing halves the monthly rate. Compare limits on the CJIS compliance software pricing page.
Questions RMS and CAD vendors ask about CJIS
Is there a CJIS certification for RMS or CAD software?
No. The FBI does not certify products or vendors. Some states run their own vendor program, and agencies still review you through the Security Addendum, background checks, training records and evidence of controls. Read what CJIS certification means before it goes into sales copy.
Does an on premises install take us out of scope?
Not entirely. The agency runs the servers, but your staff who install, upgrade and support the system can reach CJI, so they need screening and training or escorted access. Document who does what in the agreement.
Do our implementation engineers need fingerprinting?
If they have unescorted access to unencrypted CJI, yes, and several states want it for each state. Using escorted sessions or encrypting data so staff cannot reach keys can reduce the list, but each CSA decides.
Can our CAD run in a commercial cloud region?
Some states accept it with FIPS validated encryption and controlled keys, others expect a government region. The provider's agreement does not replace your controls. Ask the CSA before you quote.
How long until we can answer an RFP CJIS section?
A few weeks if your controls exist and need recording, a few months if you still need MFA on every path or a year of logs. Fingerprint processing alone can take weeks per state. The readiness check shows which areas are open today.
Answer the next RFP security section in days
Run the 12 question readiness check, see your gaps by policy area and build the first agency report. More on CJIS compliance for vendors, body camera and evidence vendors, jail management and court software vendors and CJIS compliance for SaaS companies.
What Cjis is and is not
Cjis is an independent compliance workspace, not affiliated with, endorsed by or certified by the FBI or the CJIS Division, and not legal advice. It does not run automated tests against your cloud account and it never stores CJI.